Free Access
Web Security Best Practices for Developers
Admin User
Sep 14, 2026
272 views
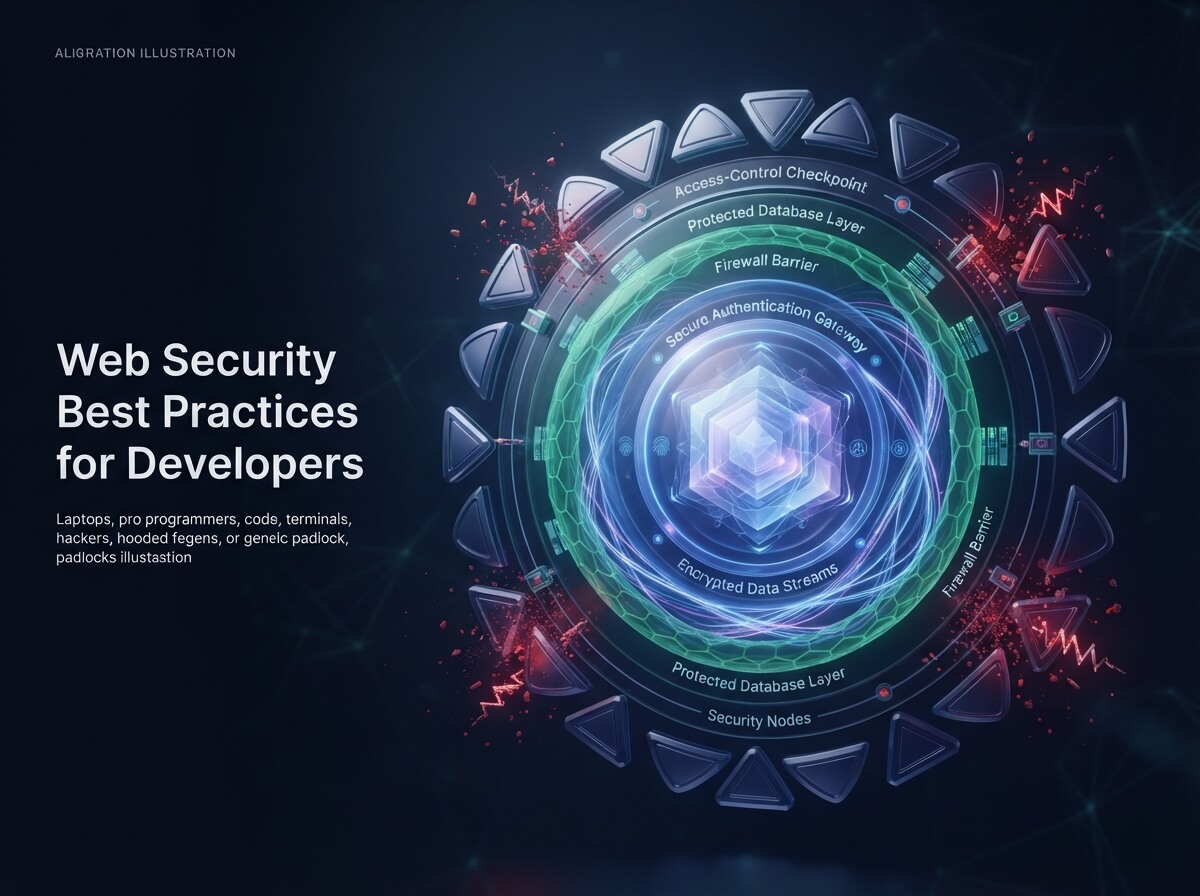
Securing Your Web Applications
Security should be a priority from day one of development. This guide covers the most common vulnerabilities and how to protect against them.
OWASP Top 10
The OWASP Top 10 lists the most critical web application security risks. Understanding these is essential for every developer.
Common Vulnerabilities
- SQL Injection: Prevent with parameterized queries
- XSS (Cross-Site Scripting): Sanitize and escape user input
- CSRF (Cross-Site Request Forgery): Use anti-CSRF tokens
- Authentication Issues: Implement proper password policies
Best Practices
- Keep dependencies updated
- Use HTTPS everywhere
- Implement proper authentication
- Validate all input
- Use security headers
\"Security is not a feature, it's a process.\"